Канареечное заявление
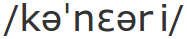
noun
*1… Небольшая певчая птица семейства вьюрковых, serinus canaria domestica, изначально распространённые на островах в северной части Атлантического океана.
2… Способ проверки небезопасных условий, изначально происходит от использования канареек в угольных шахтах для обнаружения ядовитых газов или завалов. Если канарейка умерла, то это означает, что необходимо срочно покинуть шахту. Позднее этот термин начал использоваться некоторыми поставщиками онлайн услуг для обозначения положительной декларации, регулярно обновляемой, о том, что этот поставщик не является стороной какого-либо юридического процесса. Если такая декларация не обновляется в соответствующее время, то пользователи могут сделать вывод о том, что такое канареечное заявление более не имеет места.

-----BEGIN PGP SIGNED MESSAGE-----
Hash: SHA512


Riseup positively confirms that the integrity of our system is sound: all our infrastructure is in our control, we have not been compromised or suffered a data breach, we have not disclosed any private encryption keys, and we have not been forced to modify our system to allow access or information leakage to a third party.

This canary will be re-signed on the following dates:

* February 1
* May 1
* August 1
* November 1

We will include a link to a recent news article[1] in each update to establish that the signature was not pre-generated.

h2. Frequently asked questions

Q: Are you compromised by law enforcement?

A: No. We have never permitted installation of any hardware or software monitoring on any system that we control; law enforcement has not taken our servers; does not, and has never had access to them. We would rather stop being Riseup before we did that.

Q: Couldn't the government just make you say that?

A: Forced speech is actually quite rare in the US legal context. It's usually only in cases of consumer protection where the government has been successful in compelling speech (e.g. forced cigarette warnings). Nevertheless, no they aren't forcing us to say anything.

Q: Why didn't you update your canary on time in the winter of 2016?

A: The canary was so broad that any attempt to issue a new one would be a violation of a gag order related to an investigation into a DDoS extortion ring and ransomware operation[0]. This is not desirable, because if any one of a number of minor things happen, it signals to users that a major thing has happened.

Q: Why does the new Canary not mention gag orders, FISA court orders, National Security Letters, etc?

A: Our initial Canary strategy was only harming users by freaking them out unnecessarily when minor events happened. A Canary is supposed to signal important risk information to users, but there is also danger in signaling the wrong thing to users or leading to general fear and confusion for no good reason. The current Canary is limited to significant events that could compromise the security of Riseup users.

0. https://riseup.net/about-us/press/canary-statement
1. https://www.motherjones.com/politics/2026/11/stress-test-video-podcast-election-eve-michigan-haley-stevens-polling/

-----BEGIN PGP SIGNATURE-----

iQJKBAEBCgA0FiEETgeRJo98Z+q+iPGwMEPitxOado4FAmrpi00WHGNvbGxlY3Rp
dmVAcmlzZXVwLm5ldAAKCRAwQ+K3E5p2jutOD/9HXl/GK9+MN3nIYXJvGoXdKlNb
XrSEDh02WKsSvsu1Q08bRRQ4XjGzqjHjz4uU225meq0NfcO4BIkQ8v/6oBnAb0BQ
UExaQks3dLU0Fz7lO/6978IOQqlE3QKOnVdOfAATEAB2aYBgwbTK/yCSsSYUC1ao
5Jb5qKa0ah8URpr0X98L9rMXF8CBFLyYOl3FwaHSdQr3znyV0+wVVaakoizjyumr
w/fcmCld8plagkAG5Mf8Tw3twP4Ze9s7kzKOARa6gNQwjv1OrXWS+qIe4Y3eX0Xv
Z7N7hh0WNw6g6QeLpItfXfWTOjmk4D4zfiNPJ7Olcm68iVw1Tm7NP6LNeXuXAB/d
ncIWhwubJ9FKzc9c8AfQ9CIbiL5ytkBwgofAk83jtYPVzfe8eaKi7t25qjQDqhRR
Ehc1qq3XLpVATTq1+Xnxki9rYCSXsJRHqaS9j5aZGLX1FBAK7TAo7g9lzYWrtE3u
e7U8wwzY3J16xwDxBlGZpI+/mw/NEssyy758Tj87In/4+GEgzWaj5pW6zWbNuS4J
jfVyzhy1qsHqFmme4ZeAlcTCj3VudTk9WUuQJHhRzADwR9Gc7NxwiWdST3tyHfMa
pDKtbgYJXw2zEVt+/4CejTDrgYdMU94TLFzxuBLzRVI050HqaKJK5jMa51hpTFtf
PqVNvscb7DrNrSU0VQ==
=s8If
-----END PGP SIGNATURE-----
Инструкции по проверке
Вам надлежит следовать этим инструкциям для загрузки gpg-ключа riseup и проверки его идентификатора. Затем вы можете следовать указанным ниже шагам для выполнения проверки нашего заявления:
- Загрузите подписанное канареечное заявление
Выполните в терминале следующую команду:
gpg --verify canary-statement-signed.txtВы должны получить следующий вывод:
 gpg: Signature made Fri 02 Oct 2015 09:54:28 AM PDT
 gpg:                using RSA key 0x3043E2B7139A768E
 gpg: Good signature from "Riseup Networks <collective@riseup.net>"
Убедитесь, что вывод содержит “Good signature”, а также, что идентификатор ключа совпадает с тем, который вы проверили ранее. Если текст вывода отличается, то этой информации не следует доверять.